Trust & Security
This page is for the security, compliance or procurement reviewer. It covers where Asenion runs, who can get in, how it connects to your systems, what happens to your data, and what you can check for yourself.
For what Asenion does end to end, start with What is Asenion?.
Certifications
Asenion is ISO/IEC 27001, ISO/IEC 42001 and SOC 2 Type 2 certified. Reports are available on request from support@asenion.ai.
These certifications cover Asenion’s own controls. For the AI systems you govern, the proof is the records described in What you can verify.
Where Asenion runs
Asenion is fully containerized, so you choose where it runs and where your data sits.
In a private-cloud or on-premises deployment, your governance data and model traffic stay inside your environment. Asenion connects out only to the model APIs and systems you name.
More detail: Deployment Options and, for the self-hosted testing service, Installation.
How everything connects
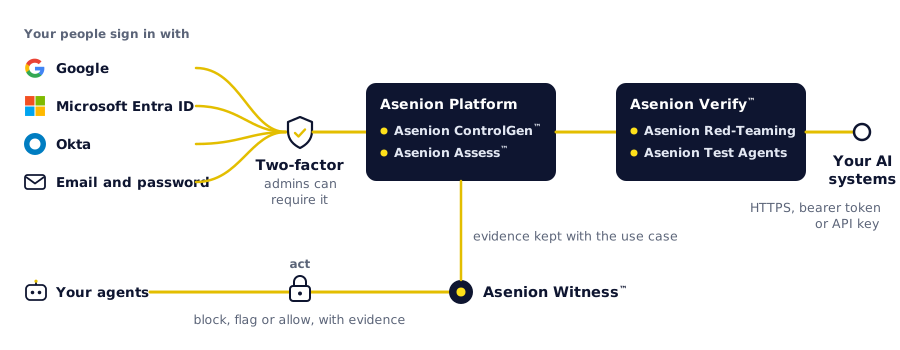
Three kinds of connection reach Asenion. Each one is authenticated.
Your people sign in
- Single sign-on with Microsoft Entra ID, Okta or Google, or email and password.
- Two-factor authentication with an authenticator app, with recovery codes. Your admins can require it for everyone in your organization.
- Roles, not shared logins, decide what each person can do. Platform-level and project-level roles cover who manages the organization, who registers an AI system, and who reviews and signs off. See User Roles.
Asenion tests your AI systems
When Asenion tests an endpoint you expose, every request goes over HTTPS and carries a credential:
- Bearer token:
Authorization: Bearer <token> - API key:
X-API-Key: <key>
Your endpoint answers a missing or invalid credential with 401 Unauthorized. You can allow unauthenticated access for local or internal use; require a credential in production. The full contract is in the endpoints reference.
Model-provider credentials stay in your environment configuration, such as an .env file or your container runtime’s secrets. Asenion calls only the model APIs you name: Azure, OpenAI, AWS Bedrock and Google Vertex, among others.
Asenion Witness checks your agents’ actions
Asenion Witness™ applies context-aware controls to agent actions in production and blocks, flags or allows them based on who is acting, on what data and for what purpose. Each decision produces a tamper-resistant witness record of what was checked, which controls applied and what was decided. See Asenion Witness.
Your data
- You choose where it lives. Pick the deployment that fits your residency and control requirements, from the table above.
- Only the people you give a role can reach it. Access follows platform and project roles.
- Reports come from the working records. Assessments, test results and reports draw on the same records your team works in, so a report shows the actual state of governance, not a reconstruction.
This page describes capabilities, not any one customer’s installation. What a deployment stores, and where, depends on the deployment you choose.
Security program
- Role-based access control
- Immutable audit trails
- Encryption at rest and in transit
- Security and assurance testing
- A written data security policy
- Security audits and risk assessments at least once a year
- Continuous vulnerability monitoring, with committed CVE response timelines
What you can verify
A security review usually ends with someone’s signed statement. With Asenion, the work itself leaves records you or your auditors can check:
- Controls carry citations to their source text and a versioned, tamper-resistant history.
- Assessments carry review trails: who answered, who reviewed, who signed off, and when.
- Tests carry results tied to the system they tested.
- Witness carries witness records, chained so that tampering is evident and the record can be verified afterward by someone who trusts no one involved.
These records are made as the work happens, not put together for an audit.
Witness shows its work
Witness blocks, flags or allows agent actions, and never silently. Every decision leaves a tamper-resistant witness record of the controls that applied and what was decided, which you or your auditors can verify.
Where to go next
- What is Asenion? The whole product on one page.
- Quickstart From access to your first governed AI system.
- Deployment Options Deployment models in detail.
- Endpoints reference The testing integration and its authentication contract.
- Glossary The platform’s vocabulary in one place.